New Research : AI Context Bombs →New: Try out Enterprise Edition free for 14 days →
Product
Platform
AWS
AWS
Azure
Azure
CI/CD
CI/CD
Google Cloud
Google Cloud
Identity
Identity
Kubernetes
Kubernetes
Workstations
Workstations
Credentials & artifacts
Connectors
Use cases
AI Attack Detection
AI Agent Oversight
Cloud & Kubernetes Breach
Insider Threat Detection
Supply Chain & CI/CD Attack
Workstation Compromise
PricingCustomers
Resources
  • ResearchAbout
  • Careers
  • Contact
PartnersCommunity Edition
Book a demoCommunity Edition

Tracebit Research

Research

Original security research from the Tracebit team.

AllResearch

Research

Context Bombs Against Abliterated AI Models

We built a new canary payload that stopped both Qwen3.8-27B and its abliterated counterpart without needing a safety refusal to fire. Then we ran 82 attacks through our AWS cyber range and found the abliterated builds reached admin in 2.3% of runs against 20.5% for the original — cutting refusals made the attacker worse, not better.
Alessandro Brucato
Sep 21, 2026
Read the research →

Research

Deception and the OpenAI / Hugging Face agentic breach

At Black Hat, OpenAI named honey tokens and deception as a key defensive investment against offensive AI agents. We map the publicly disclosed TTPs from the OpenAI / Hugging Face incident against Tracebit deception, stage by stage.

Sam Cox

Aug 10, 2026
Read the research →

Research report

Context bombs: stopping AI attackers in their tracks

We planted context bombs, short strings that trip an AI model's own safety guardrails, inside canary secrets in a live AWS environment. Across 5 frontier models and 152 runs, they cut successful attack paths from 91% to 15% - stopping attackers outright as well as detecting them.

Sam Cox

Jul 13, 2026
Read on agentic.tracebit.com ↗

Research report

Canaries against autonomous AI attackers

We pointed ten frontier models at a live AWS environment to see what canaries do against an autonomous attacker: how early they warn, how fast the models trip them, and what changes when the agent is told deception might be present.

Sam Cox

Jun 1, 2026
Read on agentic.tracebit.com ↗

Research

Detecting CI/CD Supply Chain Attacks with Canary Credentials

A single threat actor - TeamPCP - compromised a chain of widely-used open source tools: Trivy, KICS, LiteLLM, and Telnyx. This post looks at the campaign and explores the question: once you've pinned your actions and hardened your runners, what actually detects credential exfiltration from a compromised CI/CD pipeline?

Alessandro Brucato
Apr 2, 2026
Read the research →

Research

Azure Detection Engineering: Log idiosyncrasies you should know about

We share a few inconsistencies found in Azure logs which make detection engineering more challenging.

Michael Aldridge

Mar 10, 2026
Read the research →

Research

Short Term vs Long Term Canary Credentials

I'll explore the trade-offs between long and short term canary credentials for threat detection and explain why I think short term credentials are increasingly the right choice for most deployments.

Gemma Jacobson

Nov 11, 2025
Read the research →

Research

Code Execution Through Deception: Gemini AI CLI Hijack

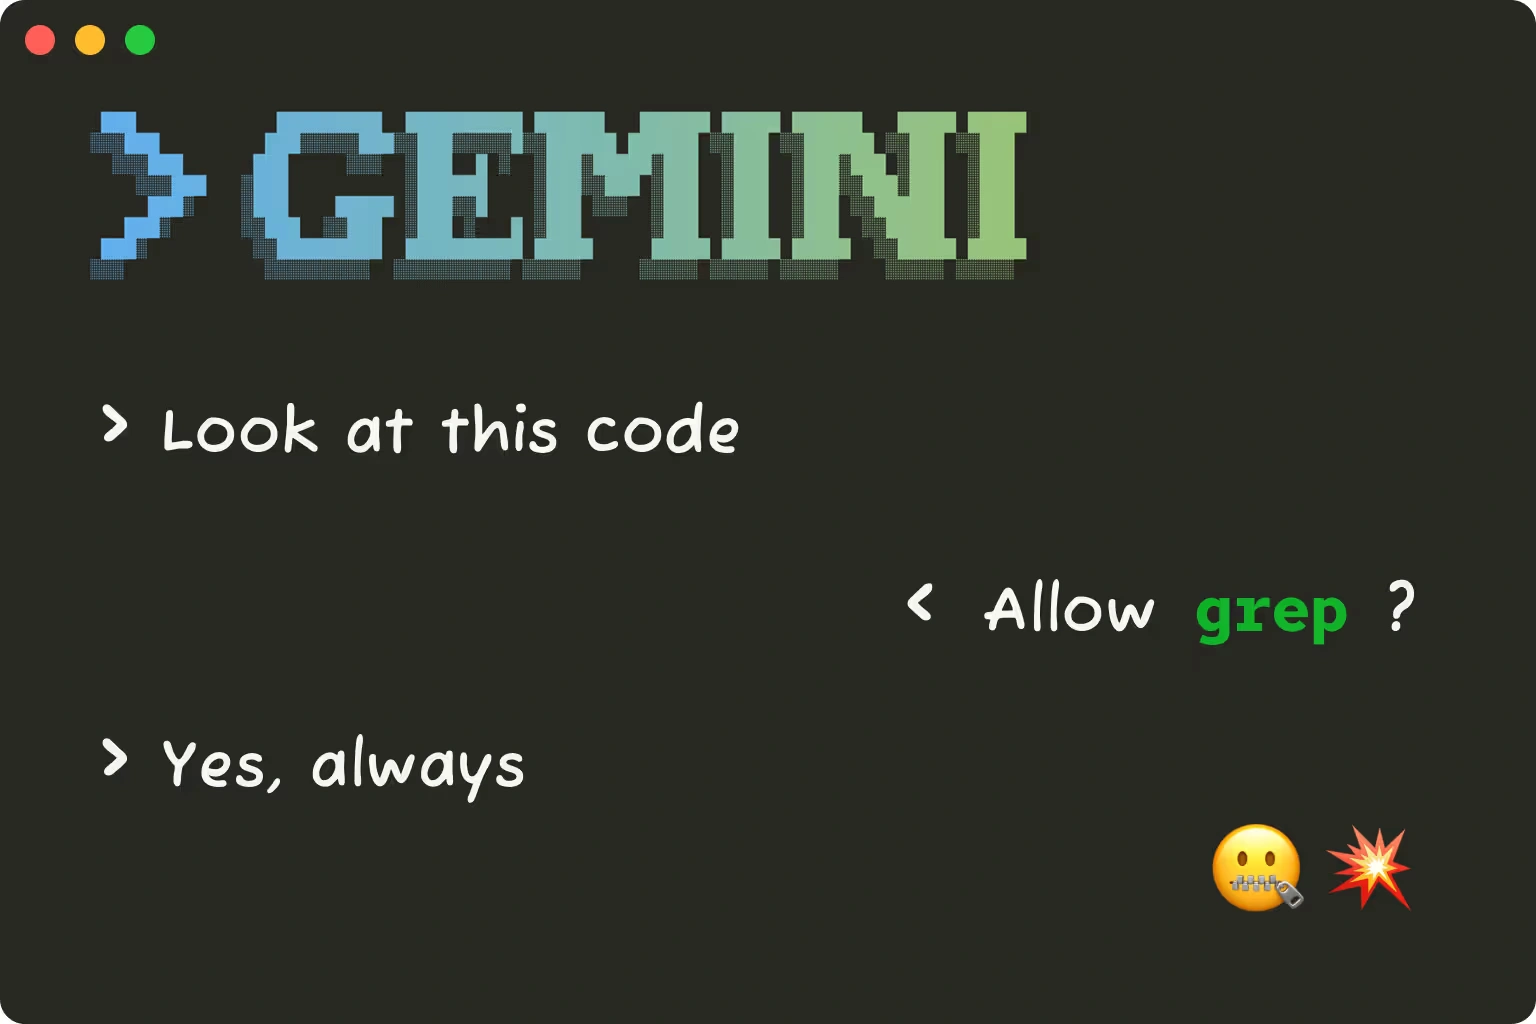
Tracebit discovered a silent attack on Gemini CLI where, through a toxic combination of prompt injection, misleading UX and missing validation, inspecting untrusted code consistently leads to execution of malicious commands - enabling silent credential theft and much more.

Sam Cox

Jul 28, 2025
Read the research →

Research

Breaching the Data Perimeter: CloudTrail as a mechanism for Data Exfiltration

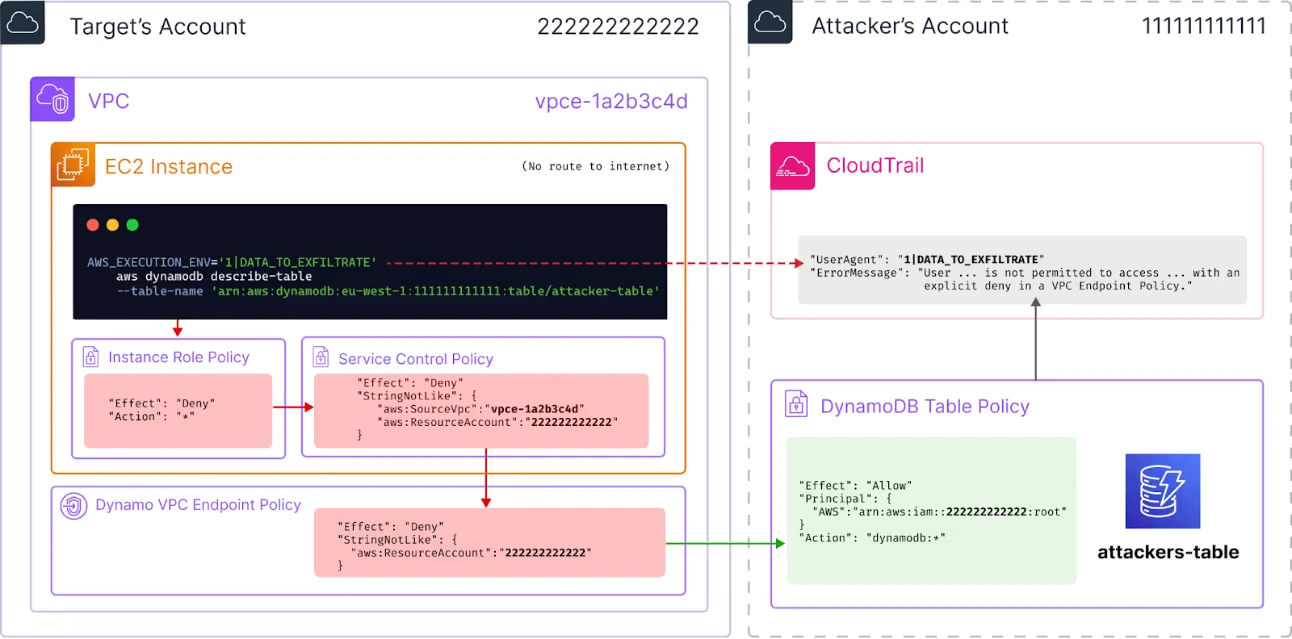
We share a - now fixed - AWS vulnerability that would have enabled potentially undetectable data exfiltration from even the most locked down of AWS accounts by leveraging the audit trail itself to stealthily leak data.

Sam Cox

Oct 15, 2024
Read the research →

Research

The Security Canary Maturity Model

We lay out the different levels of maturity your organization may be at in their Security Canary Maturity, as well as discussing the value in maturity models themselves.

Rami McCarthy

Sep 10, 2024
Read the research →

Research

Canary Infrastructure vs. Real World TTPs

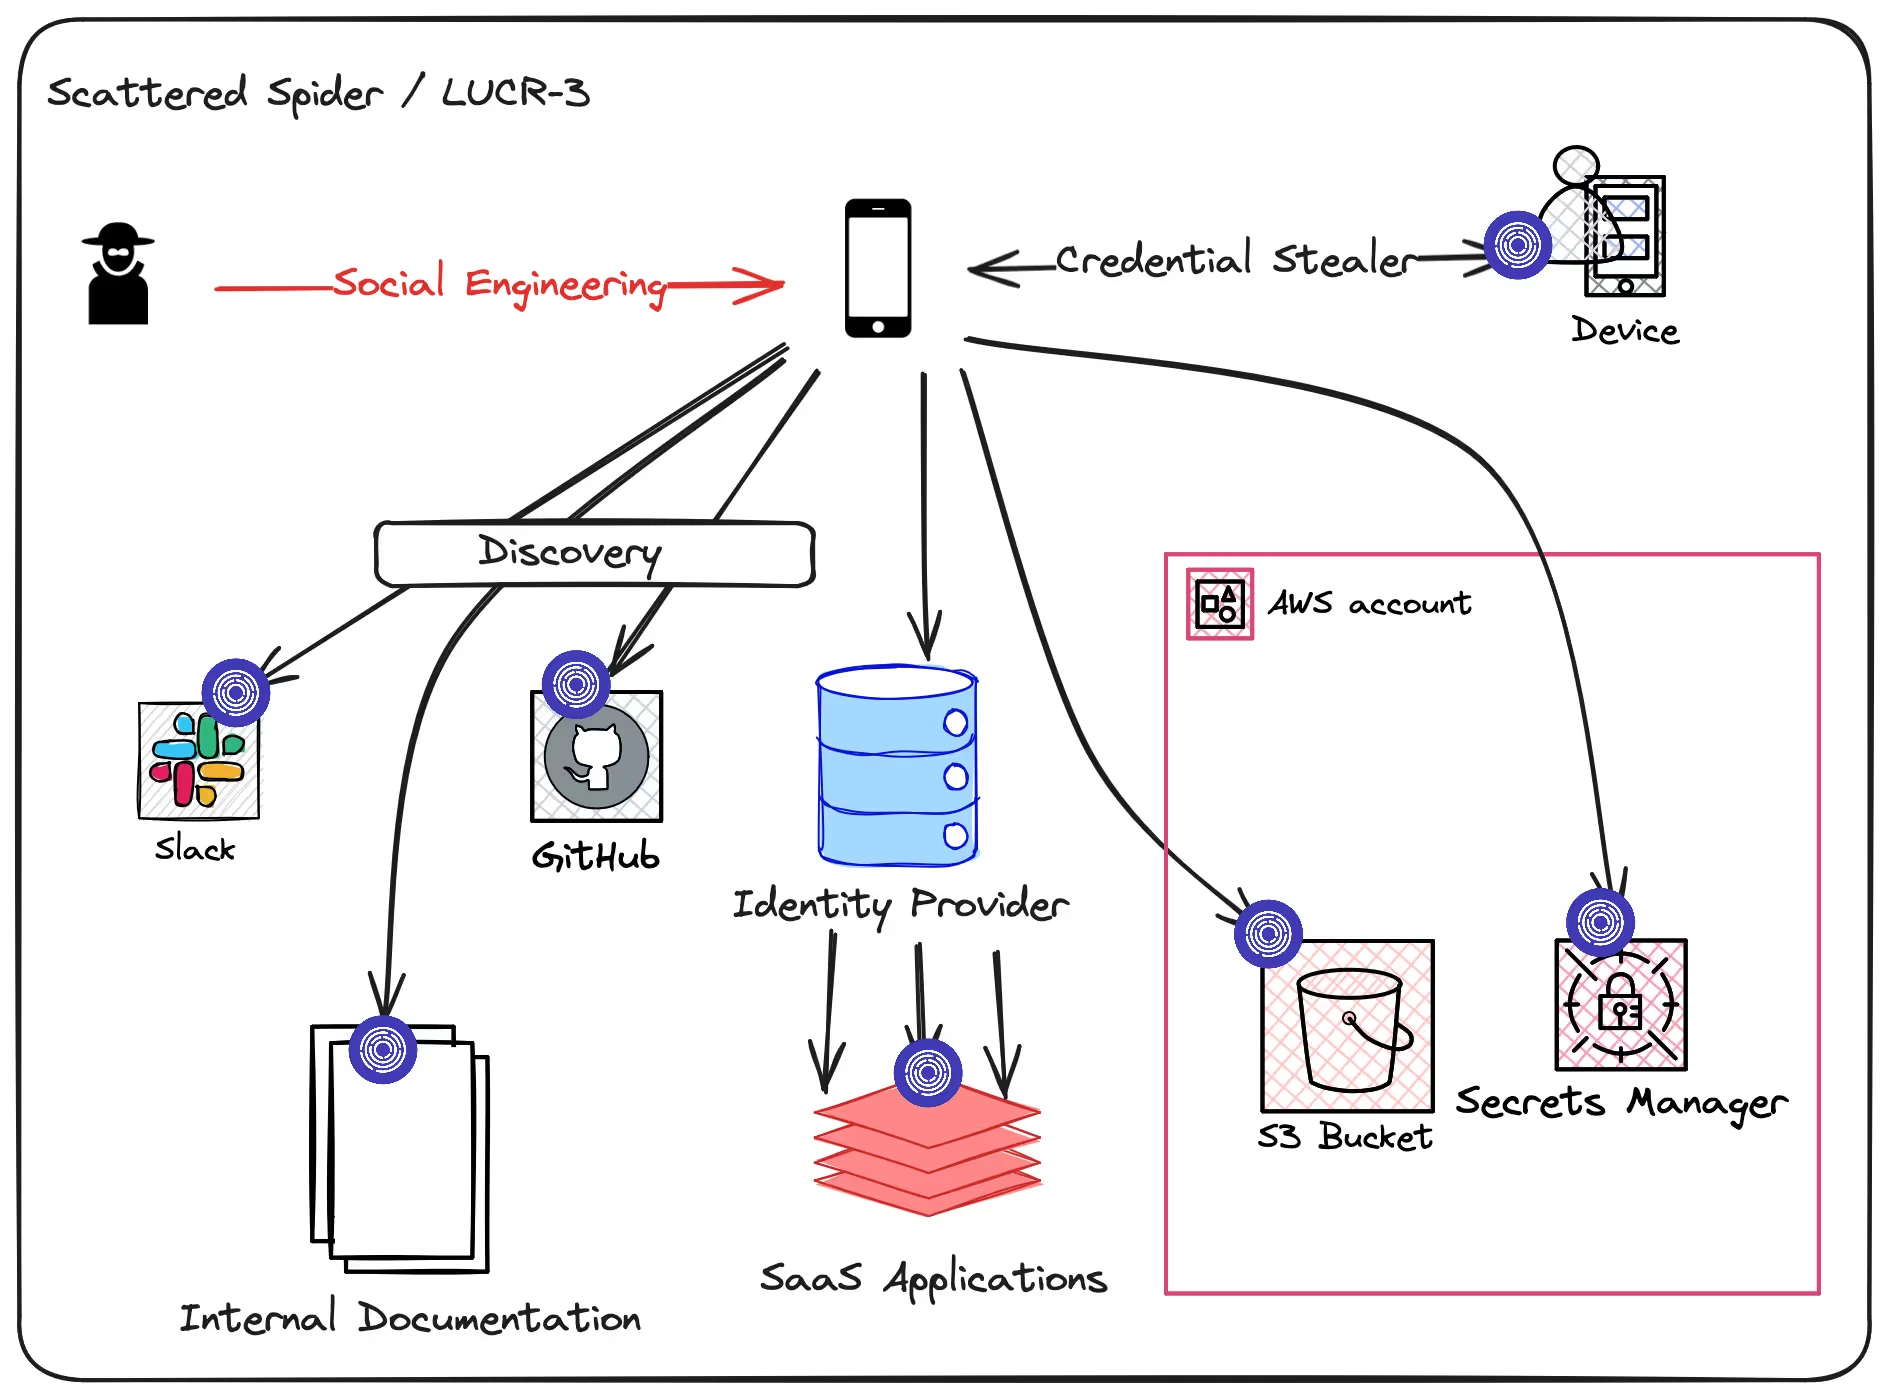
We investigate three recent AWS security incidents and discuss how canaries could help you detect these early, and throughout the attack lifecycle.

Rami McCarthy

Aug 13, 2024
Read the research →

Research

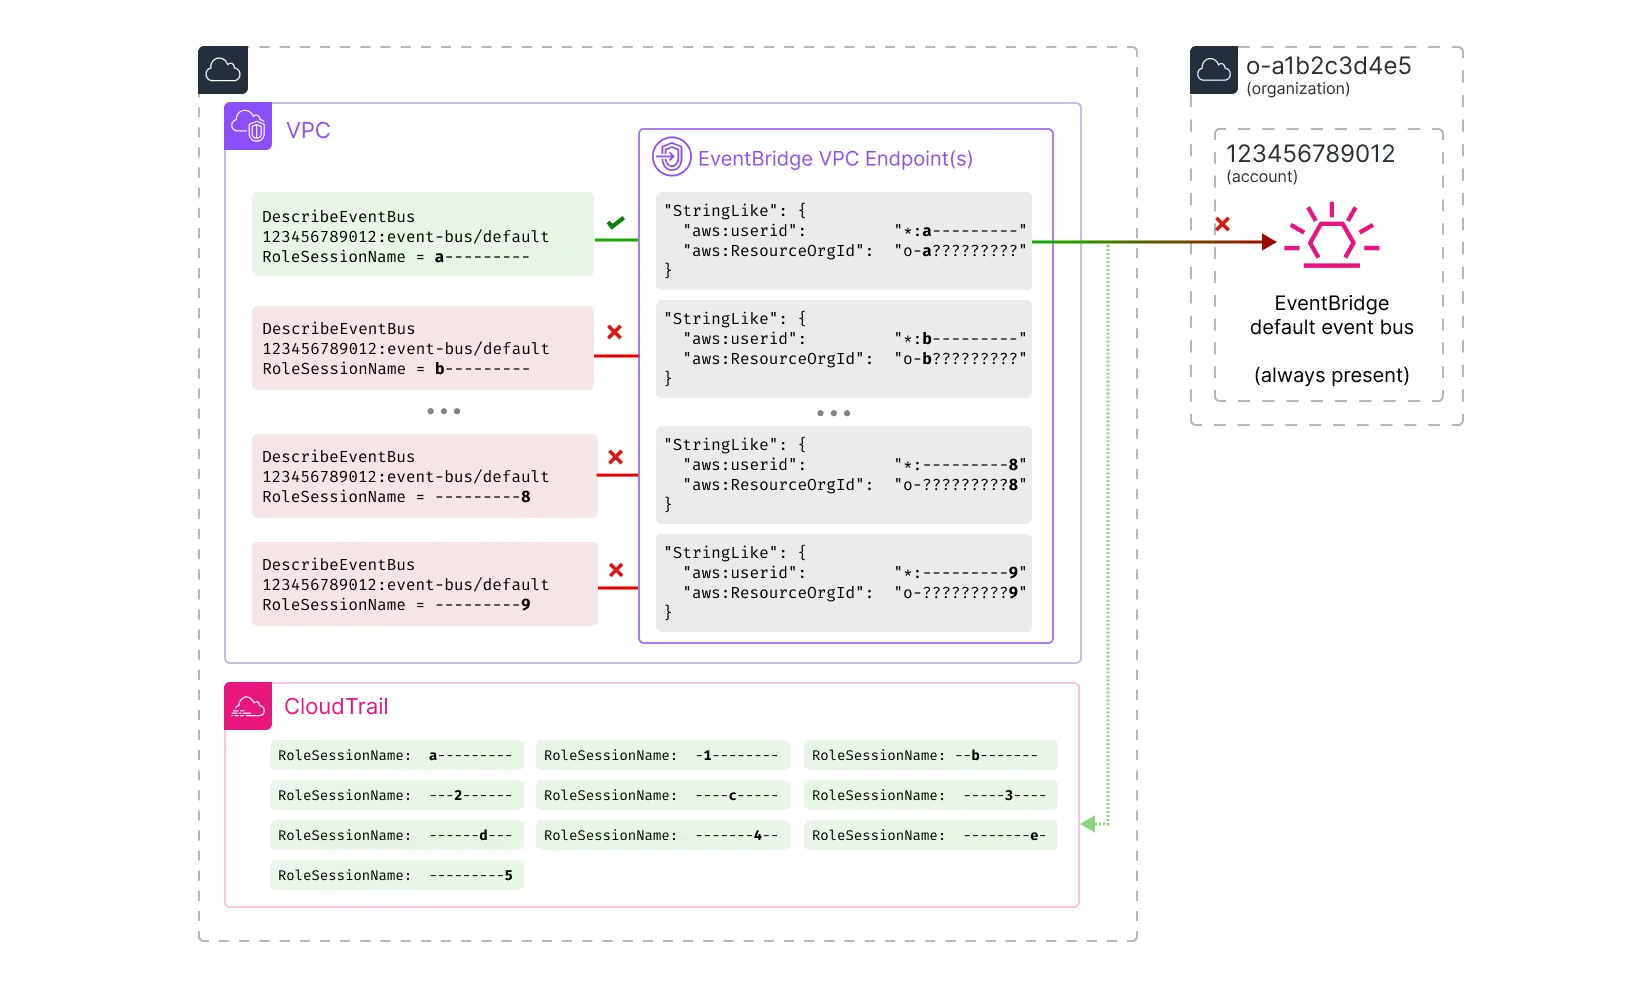
NO_WILDCARD: How I discovered the Organization ID of any AWS Account

Our latest research into VPC Endpoint Policy causes AWS to introduce significant changes!

Sam Cox

Jul 22, 2024
Read the research →

Research

A hard look at GuardDuty shortcomings

Is GuardDuty all you need for AWS threat detection? We’ve asked our friend Rami McCarthy to dive into GuardDuty’s performance and consider the potential place for Canary Infrastructure.

Rami McCarthy

Jul 16, 2024
Read the research →

Research

Canary AWS credentials: Beyond a token effort

What to think about when implementing canary AWS credentials in 2024 and beyond

Sam Cox

May 3, 2024
Read the research →

Research

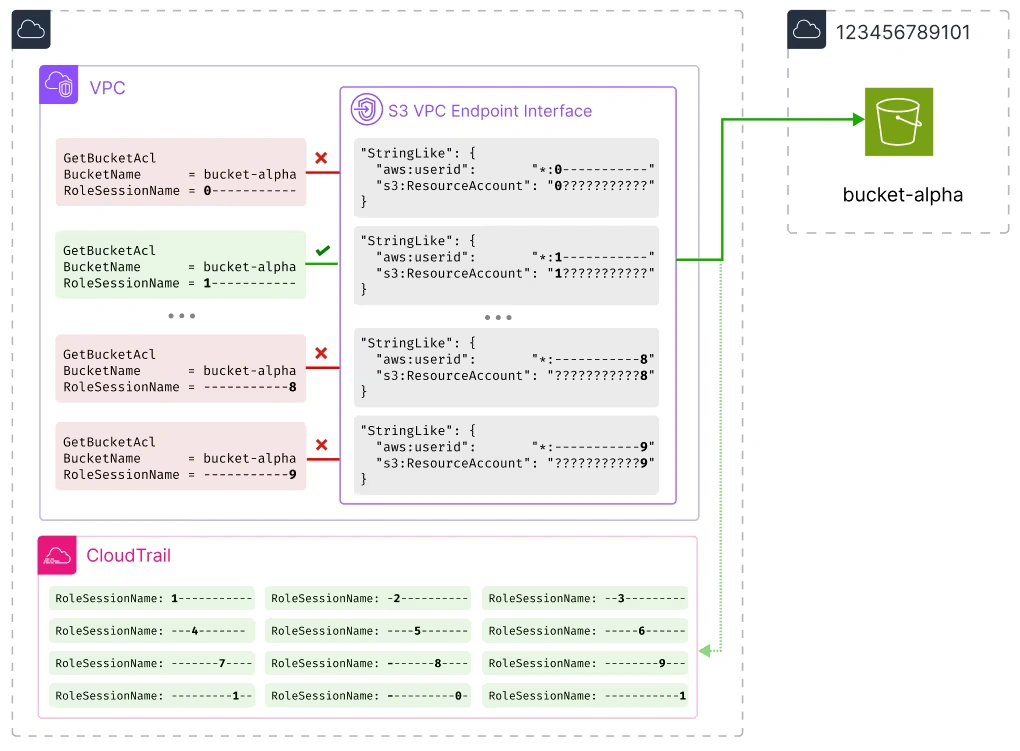
How to find the AWS Account ID of any S3 Bucket

A technique to find the Account ID of a private S3 bucket.

Sam Cox

Feb 22, 2024
Read the research →

Research

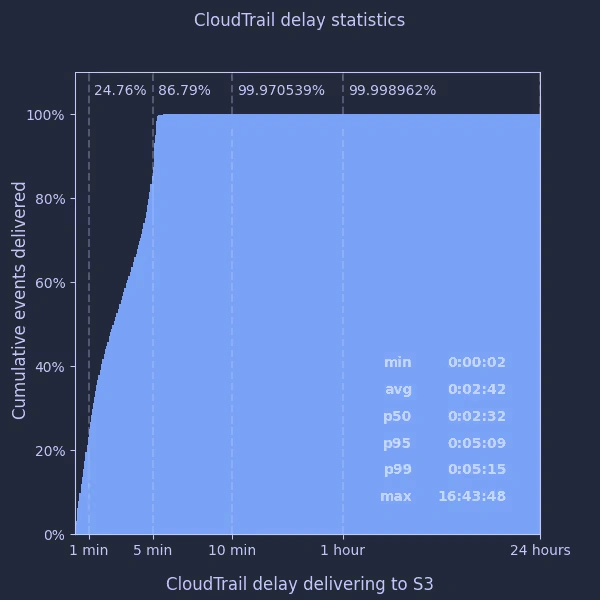
How fast is CloudTrail today? Investigating CloudTrail delays using Athena

Investigating how long CloudTrail takes to deliver events in 2023.

Sam Cox

Nov 27, 2023
Read the research →

Research

Honeypots for Intrusion Detection

A deep dive into what Honeypots are, why they're useful and how they're used for intrusion detection.

Andy Smith

Nov 13, 2023
Read the research →
Soc 2 Type 2 imageCheckmark imageAWS Qualified software illustration
  • G2★4.9 / 5
  • Gartner Peer Insights★4.9 / 5
PLATFORM
AWS
Azure
CI/CD
Google Cloud
Identity
Kubernetes
Workstations
Credentials & artifacts
Connectors
USE CASES
AI Attack Detection
AI Agent Oversight
Cloud & Kubernetes Breach
Insider Threat Detection
Supply Chain & CI/CD Attack
Workstation Compromise
COMPANY
CustomersResearchAboutCareersContactFAQStatusCommunity EditionFree Enterprise Edition Trial
SOCIAL
© 2026 Tracebit
Privacy PolicyTerms of ServiceCookie Settings
Ask Tracebit

Loading chat…

Contact the team