Live session · Wednesday 11 November 2026 · 19:00 GMT / 14:00 ET / 11:00 PT
Building a Custom Deception Strategy for Your Environment
Most deception deployments stall at the same point. Getting a handful of canaries out is straightforward. Covering the rest of the estate convincingly is where teams run out of time.
Tracebit co-founders Andy Smith and Sam Cox walk through how to close that gap: new research on what measurably slows an AI attacker down, canary files for the systems that give you no telemetry today, and a method for building a deception plan that matches your environment instead of a generic one.
Can't make it live? Register anyway and we'll send you the recording.
Speakers
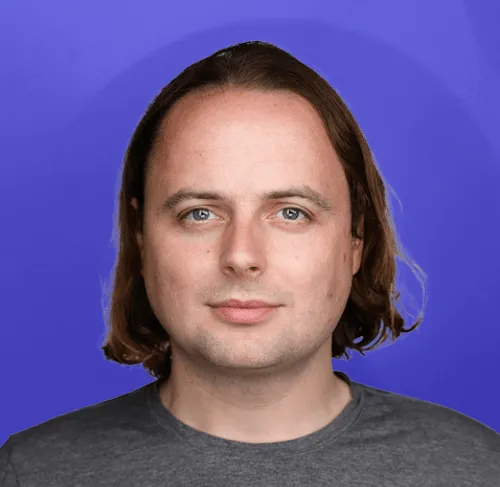
Andy Smith
Co-founder and CEO, Tracebit
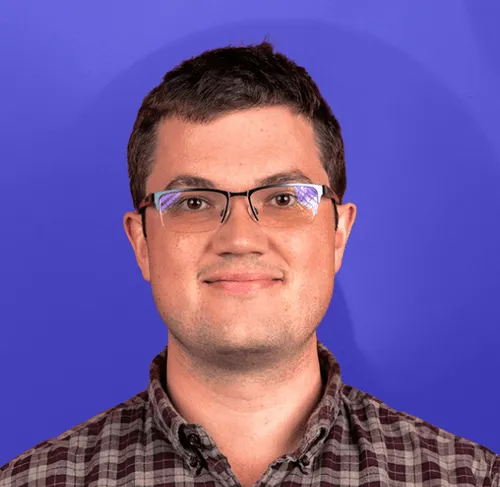
Sam Cox
Co-founder and CTO, Tracebit
Save your seat
Tracebit is used by security teams at Docker, Riot Games, Coveo, Synthesia, Cresta and Zepz.
- Date
- Wednesday 11 November 2026
- Time
- 19:00 GMT / 14:00 ET / 11:00 PT
- Length
- 45 minutes
What we'll cover
New research: context bombs that slow an AI attacker down
We tested nine deception techniques on seven frontier models in 773 AWS assessments. Sam will go through what the numbers showed about completed objectives, model spend and time to objective, and which techniques slowed down malicious AI agents across every model.
Tracebit Artifacts: file-based canaries give you visibility into all types of systems - including SaaS
Artifacts are files that carry a canary. Anywhere a file can sit, a canary can now sit with it: SaaS applications with no useful security logging, file shares, embedded devices, developer workstations. We'll cover the file types available at launch and what makes a decoy file survive contact with a real attacker.
Building a deception plan with an agent and the Tracebit MCP
Deception works when it is specific to your environment, which is exactly the part that doesn't scale by hand. We'll show the workflow end to end: feeding an AI agent your network diagrams and organizational documents, having it reason about what an attacker would go after, then connecting it to Tracebit's MCP to generate and place artifacts that match what's already there.
A walkthrough in a live environment
Andy will run you through the entire motion in a live demo.
Who this is for
- Security engineers and detection engineers who own coverage and are tired of writing rules for behavior they can't see.
- SOC leaders looking for high-fidelity signals across various systems.
- Security leaders who have read CISA's decoy guidance and want a practical starting point.
No prior experience with deception technology is assumed.