High-fidelity detection. Start this afternoon.
Cyber Decoys
Detect attackers inside your environment with cyber decoys. Tracebit deploys security canaries: realistic credentials and resources that look valuable to attackers but have no legitimate business use. Attempts to use canary credentials or access decoy resources trigger alerts with the context your team needs to investigate and respond.
CISA recommends cyber decoys to strengthen detection and response alongside Zero Trust. Tracebit helps you put its cyber decoy guidance into practice with canaries that fit your environment and send alerts to the security tools you already use. Start with one decoy and expand from there.
“Canary-based detection is a critical layer in
Docker’s defense-in-depth strategy. Tracebit makes
deploying and managing deception at scale practical.”

Mark Lechner
CISO, Docker
“As our environment evolves and attacker behavior and knowledge evolves it’s important that we stay ahead of the game with Tracebit.”

Chris Hymes
CISO, Riot Games
“It’s one of those rare tools that feels like it was built by people who deeply understand the platform and the real world problems defenders face. A true work of art.”

Jean-Philippe Lachance
Staff Security Specialist in R&D, Coveo
Request a free trial
Put CISA's cyber decoy guidance to work in your environment.
How it works
Place cyber decoys where attackers look next
Canaries help put Zero Trust's “assume breach” principle into practice. When attackers get past your defenses, you need a way to detect them inside your environment. Tracebit places decoy cloud resources, identities and credentials across the systems they explore, including cloud accounts, workstations and CI/CD pipelines. Each decoy gives you another opportunity to detect activity that normal work should never require.
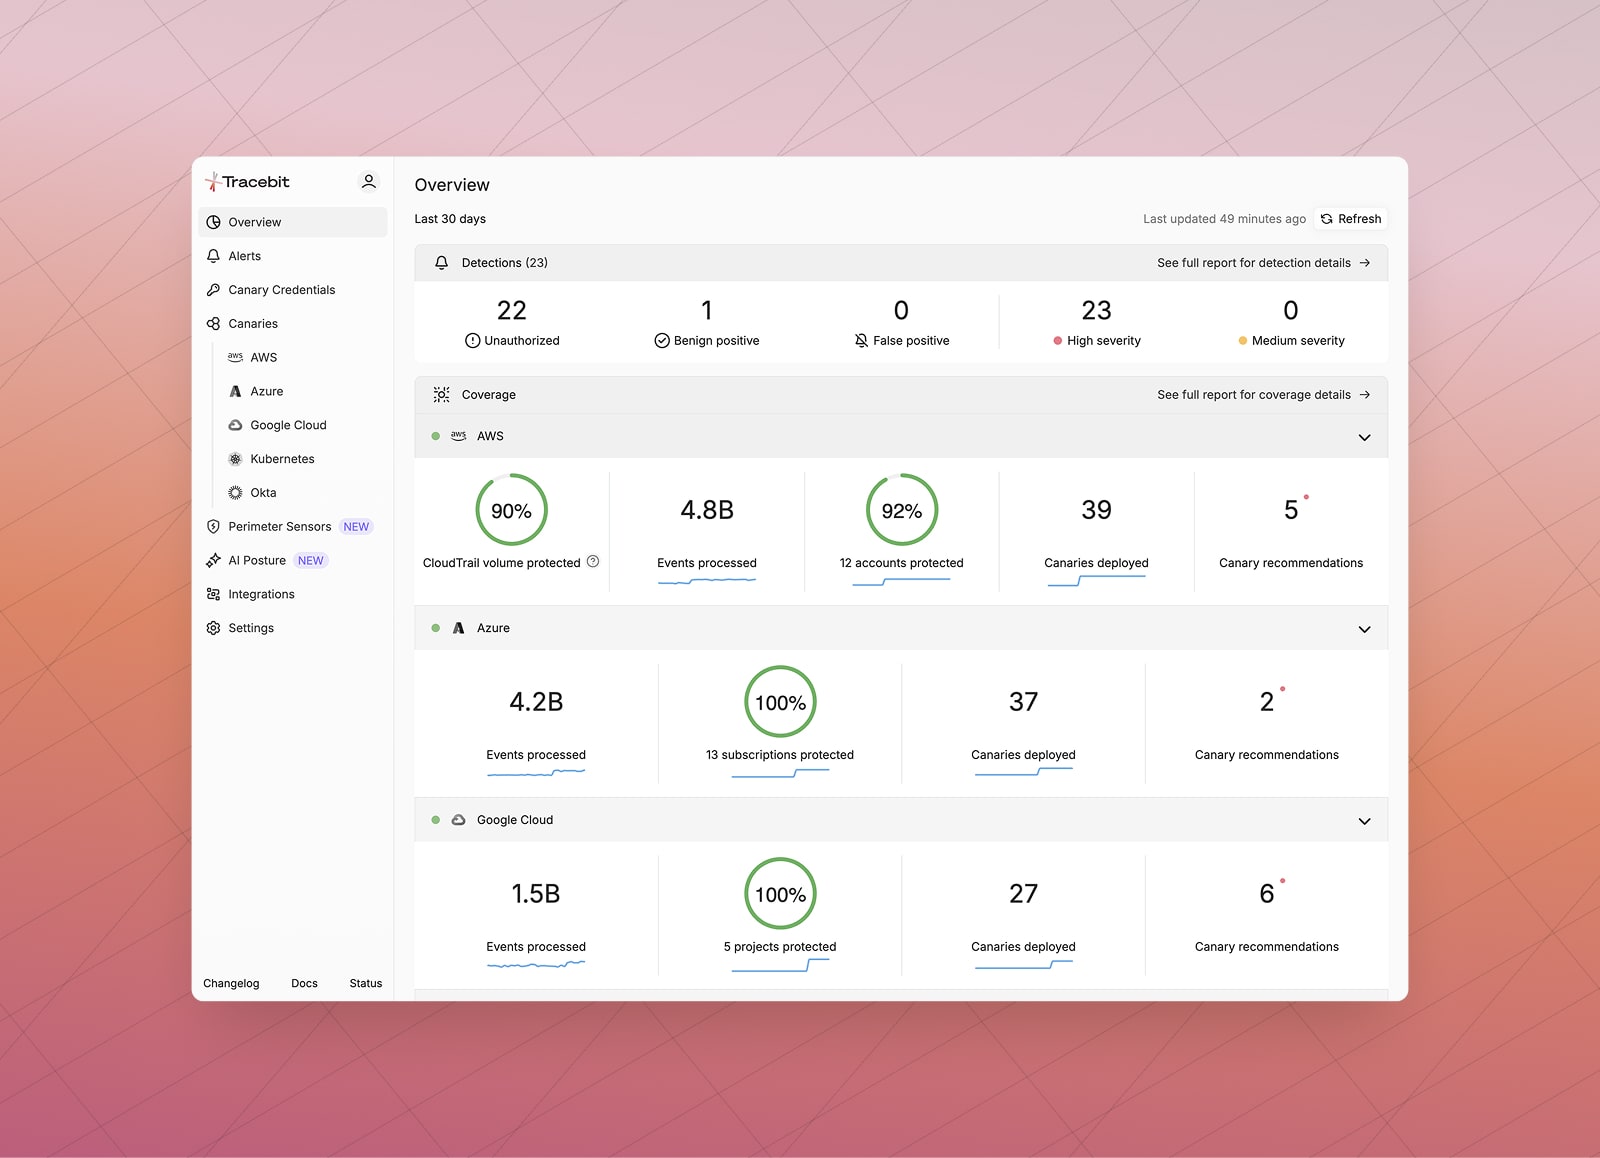
Reduce detection time with high-fidelity alerts
Cyber decoys create a clear signal by monitoring assets that have no legitimate business use. CISA says of honeytokens: “Any interaction strongly suggests malicious or otherwise unauthorized activity.” Tracebit sends canary alerts to your existing SIEM and SOAR with context about the decoy and the activity that triggered it, helping your team investigate and respond sooner.
Expose attackers using legitimate tools and credentials
Attackers can use native tools and valid credentials to blend into everyday activity. CISA highlights cyber decoys as particularly valuable against these living off the land techniques, where signatures are less effective. Tracebit alerts when an attacker accesses a decoy resource or tries a canary credential, even when the tool making the request is legitimate.
Deploy your first cyber decoy this afternoon
Start with a canary credential on one workstation, deployed through your existing device management tools. Test the alert, then expand across your fleet, cloud accounts and pipelines. Tracebit automates canary updates and uses AI to help decoys fit their surroundings as your environment changes. You can start detecting while you build broader coverage.
Make attackers spend more time and resources
CISA recognises that decoys can divert attackers and consume their time and resources. Human attackers who suspect canaries are present have to weigh each promising credential against the risk of detection. AI agents following false leads can spend tool calls, processing time and tokens on decoys. Those detours create more opportunities for your team to detect and respond.